Configure
SimpleSAMLphp Authentication
SimpleSAMLphp is a third-party PHP application that deals with authentication. The main focus of SimpleSAMLphp is providing support for SAML 2.0, but it supports a wide range of other protocols, such as Shibboleth, CAS, OpenID, WS-Federation or OAuth.
Step 1: Install SimpleSAMLphp
More information about SimpleSAMLphp here: https://simplesamlphp.org
Make sure you install it on the same domain and subdomain as FileRun, so that FileRun ca access the same browser cookies as SimpleSAMLphp. If you are unsure what that means, just install SimpleSAMLphp in a subfolder inside the FileRun installation folder.
Step 2: Configure SimpleSAMLphp with your iDP
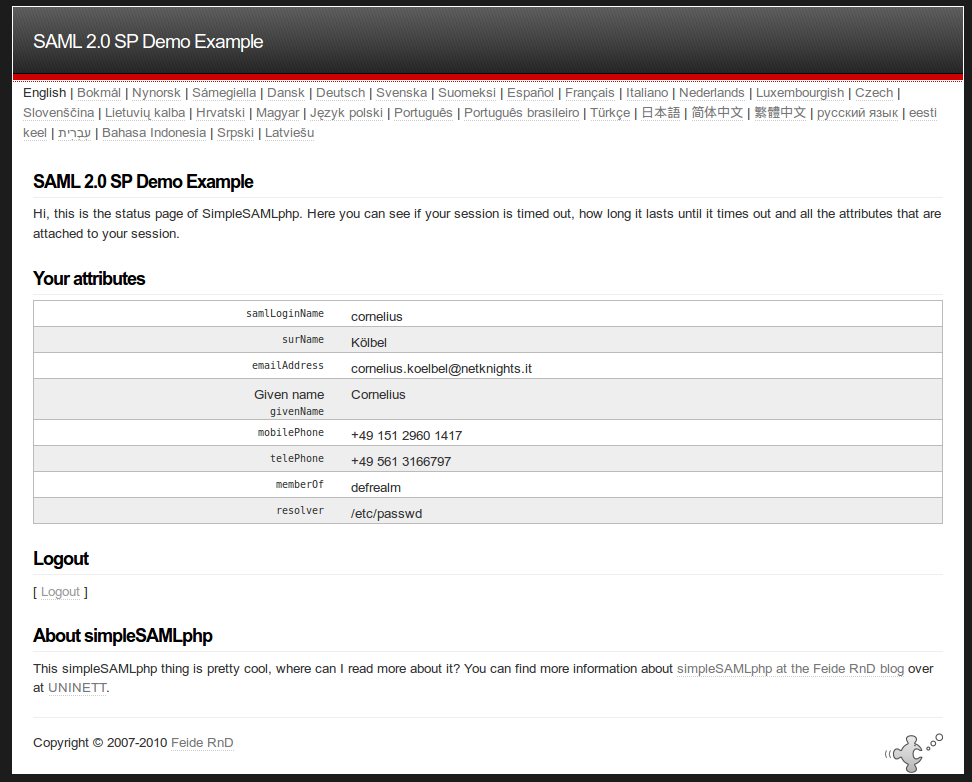
Once you have configured SimpleSAMLphp with your identity provider, test your settings, and make sure you can sign in successfully, and that you are seeing the user information, like in this screenshot:
Step 3: Configure FileRun
You can easily activate and configure the plugin directly from FileRun's
control panel, under System configuration →
User login and registration.
Using the attributes you are seeing inside SimpleSAMLphp, configure the FileRun mapping.
As per the example screenshot
Username attribute mappingwould besamlLoginNameFirst name attribute mappingwould begivenNameLast name attribute mappingwould besurNameE-mail attribute mappingwould beemailAddressGroup names attribute mappingwould bememberOf
But the attributes returned from your identity provider can be completely different. The above is just an example to help you understand how the mapping is done.